Fixed: "NU1903: Warning As Error: Package 'Newtonsoft.Json' 12.0.3 has a known high severity vulnerability"

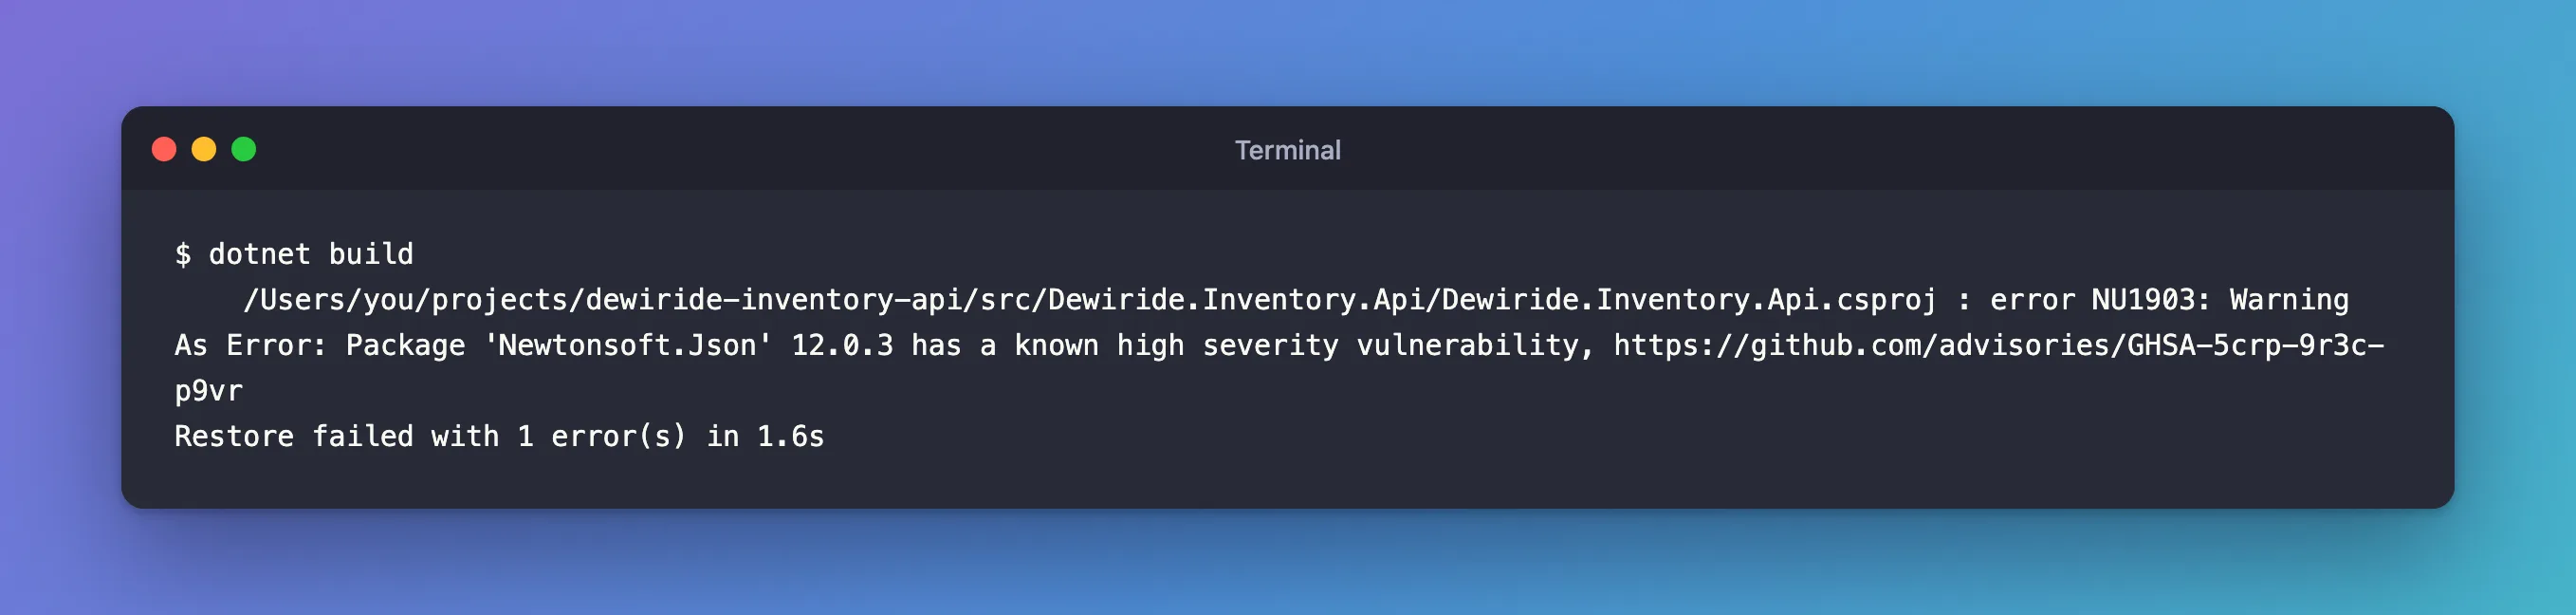
error NU1903: Warning As Error: Package 'Newtonsoft.Json' 12.0.3 has a known high severity vulnerability, https://github.com/advisories/GHSA-5crp-9r3c-p9vr NuGet's built-in audit found a published security advisory for a package version the project uses, and because warnings were errors, restore stopped. The fix is one version change. Getting there took me two failed attempts first, and both are worth knowing.
What I Was Doing
In a .NET 10 solution with TreatWarningsAsErrors and Central Package Management, I added version 12.0.3 of Newtonsoft.Json to the web API:
dotnet package add Newtonsoft.Json --version 12.0.3 --project src/Dewiride.Inventory.Api
What I Expected
The package added, and a successful restore.
What I Got
error: NU1903: Warning As Error: Package 'Newtonsoft.Json' 12.0.3 has a known high severity vulnerability, https://github.com/advisories/GHSA-5crp-9r3c-p9vr
info : PackageReference for package 'Newtonsoft.Json' added to '/Users/you/projects/dewiride-inventory-api/src/Dewiride.Inventory.Api/Dewiride.Inventory.Api.csproj' and PackageVersion added to central package management file '/Users/you/projects/dewiride-inventory-api/Directory.Packages.props'.
log  : Failed to restore /Users/you/projects/dewiride-inventory-api/src/Dewiride.Inventory.Api/Dewiride.Inventory.Api.csproj (in 732 ms).
Both at once: the reference was added to the project and the version to Directory.Packages.props, and restore failed. From then on, every build stopped the same way:
    /Users/you/projects/dewiride-inventory-api/src/Dewiride.Inventory.Api/Dewiride.Inventory.Api.csproj : error NU1903: Warning As Error: Package 'Newtonsoft.Json' 12.0.3 has a known high severity vulnerability, https://github.com/advisories/GHSA-5crp-9r3c-p9vr

Restore failed with 1 error(s) in 1.6s
What I Checked
What NU1903 means. Microsoft's NU1901-NU1904 page: "A package restored for your project has a known vulnerability." The number is the severity: NU1903 is high. The link goes to the advisory itself, which says which versions are affected and which version fixes it.
Why it's an error. NuGet's warnings follow TreatWarningsAsErrors too, hence "Warning As Error". The same page offers <WarningsNotAsErrors>NU1901;NU1902;NU1903;NU1904</WarningsNotAsErrors> to keep them as warnings, but a build that stops on a known vulnerability is doing its job.
First mistake: making the report ignore the setting. I wanted the vulnerability report without the error, so I tried passing the property to the list command:
Unrecognized command or argument '-p:TreatWarningsAsErrors=false'.
dotnet package list doesn't take MSBuild properties. And without the option, it couldn't list anything: in .NET 10 it restores first, and that restore failed on NU1903.
What worked: skip the restore. --no-restore uses the result of the last restore:
Project `Dewiride.Inventory.Api` has the following vulnerable packages
   [net10.0]:
   Top-level Package      Requested   Resolved   Severity   Advisory URL
   > Newtonsoft.Json      12.0.3      12.0.3     High       https://github.com/advisories/GHSA-5crp-9r3c-p9vr

The given project `Dewiride.Inventory.Data` has no vulnerable packages given the current sources.
One package, one project, severity High.
Why It Happens
Newtonsoft.Json 12.0.3 has a published high-severity advisory. NuGet checks every restore against the known advisories and reports this one as NU1903, which is a warning; TreatWarningsAsErrors turns it into an error. The reference was written before the restore ran, so the project kept it, and every restore, and with it every build, stopped from then on.
The Fix
The page's solution: "Upgrading to a newer version of the package is likely to resolve the warning."
Second mistake: updating without a version. dotnet package add without --version normally takes the newest version. Here it failed with the same NU1903 and changed nothing, because it restores the current, vulnerable state on the way.
What worked: name the version.
dotnet package add Newtonsoft.Json --version 13.0.4 --project src/Dewiride.Inventory.Api
info : Package 'Newtonsoft.Json' is compatible with all the specified frameworks in project '/Users/you/projects/dewiride-inventory-api/src/Dewiride.Inventory.Api/Dewiride.Inventory.Api.csproj'.
log  : Restored /Users/you/projects/dewiride-inventory-api/src/Dewiride.Inventory.Api/Dewiride.Inventory.Api.csproj (in 730 ms).
With Central Package Management, the version changed in Directory.Packages.props, to 13.0.4, the newest stable version. dotnet package update --vulnerable can choose the version for you, but under warnings as errors it needs a documented workaround; Fixed: "dotnet package update: Unhandled exception: Specified method is not supported." covers it.
After the Fix
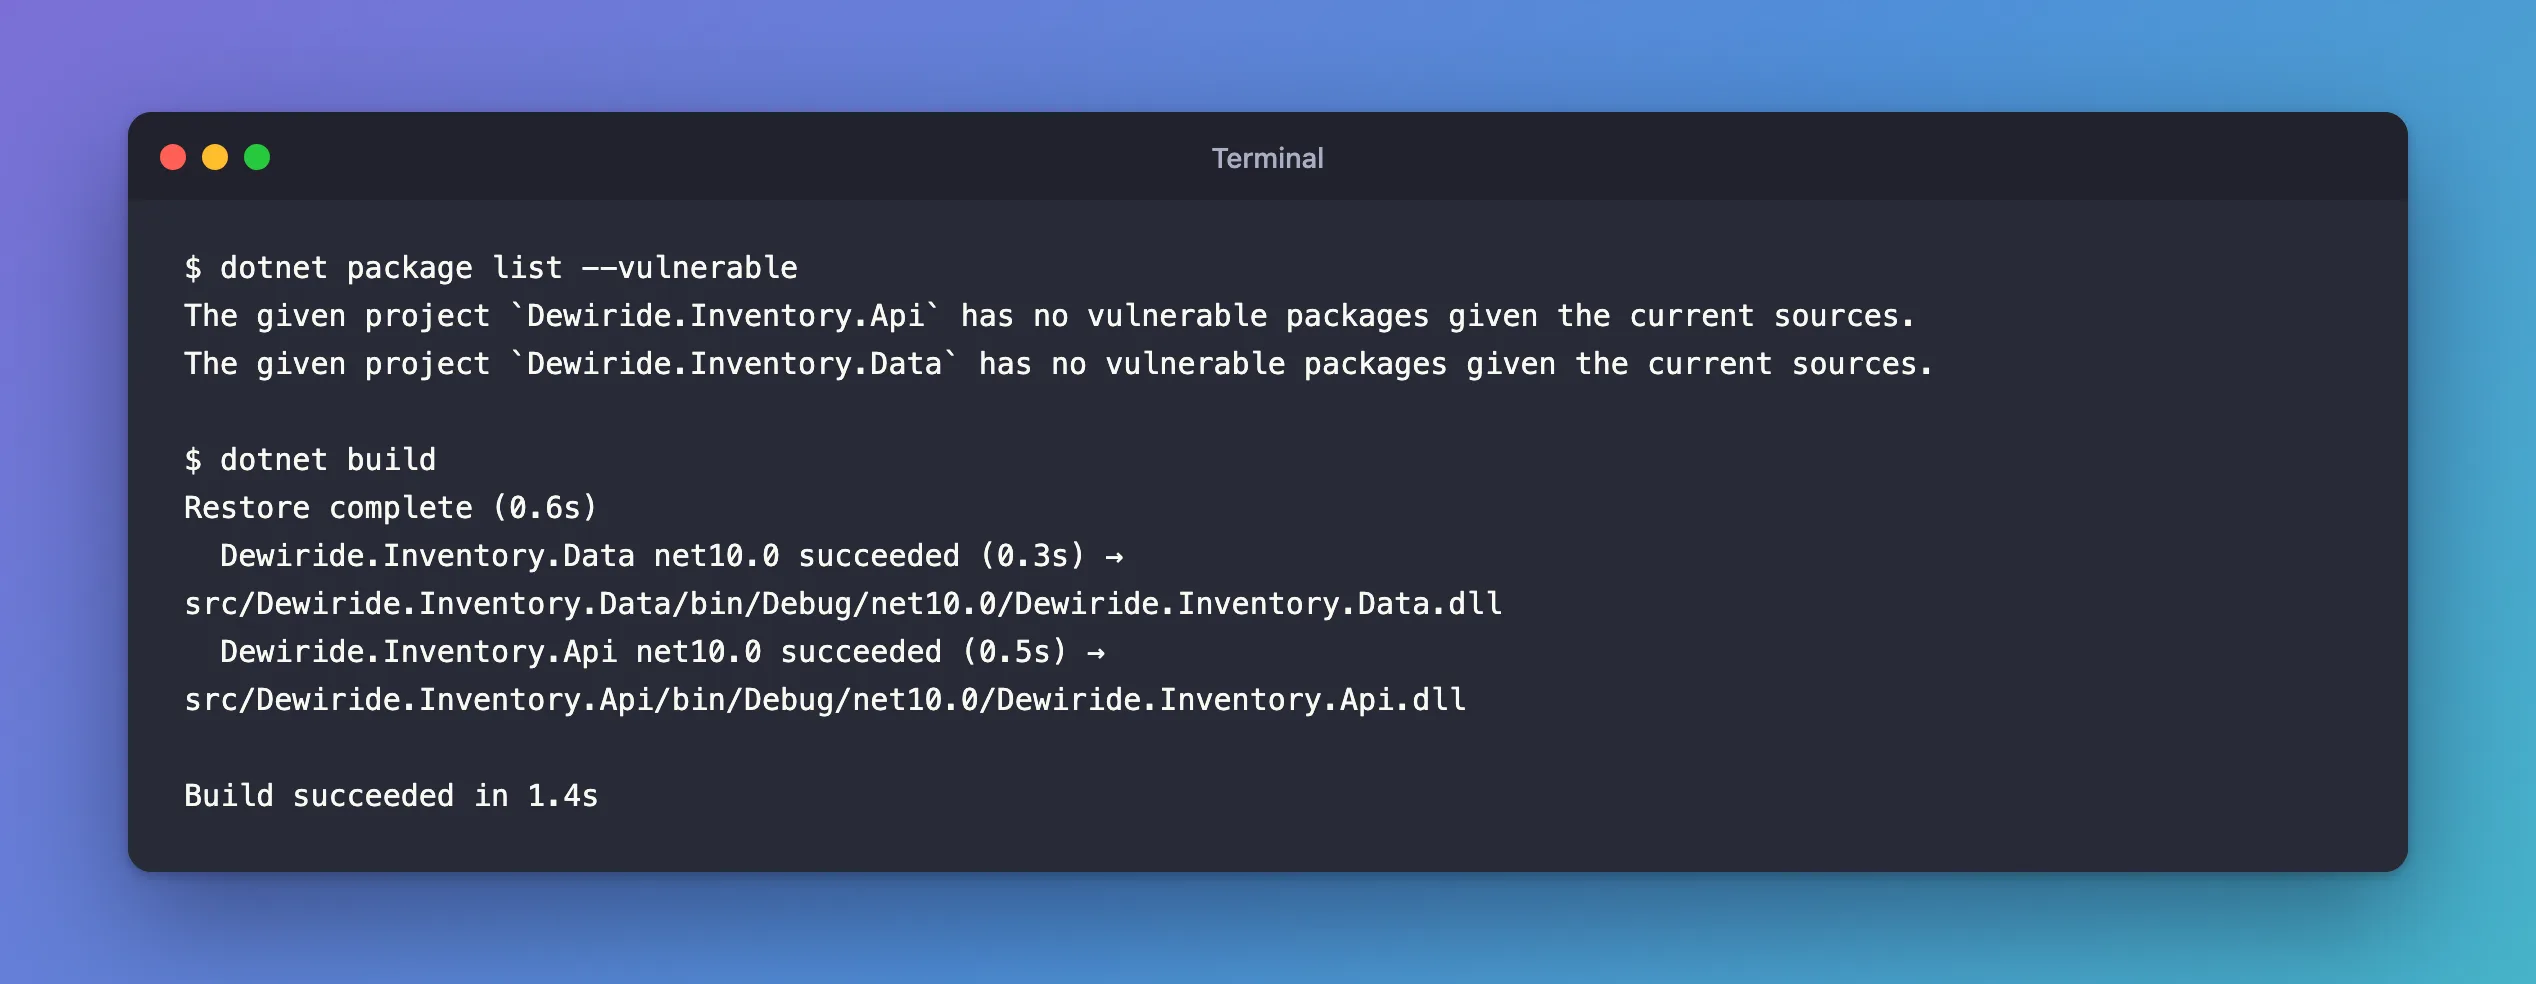
The given project `Dewiride.Inventory.Api` has no vulnerable packages given the current sources.
The given project `Dewiride.Inventory.Data` has no vulnerable packages given the current sources.
Restore complete (0.6s)
  Dewiride.Inventory.Data net10.0 succeeded (0.3s) → src/Dewiride.Inventory.Data/bin/Debug/net10.0/Dewiride.Inventory.Data.dll
  Dewiride.Inventory.Api net10.0 succeeded (0.5s) → src/Dewiride.Inventory.Api/bin/Debug/net10.0/Dewiride.Inventory.Api.dll

Build succeeded in 1.4s
Common Mistakes
| Mistake | What happens | Do this instead |
|---|---|---|
Adding NU1903 to NoWarn | The vulnerability stays, silently | Update the package |
Updating without --version while restore fails | Fails with the same error | Pass the safe version explicitly |
Running the report without --no-restore | You get the restore error instead | dotnet package list --vulnerable --no-restore |
| Assuming a direct reference is the only cause | With .NET 10, transitive packages are audited too | Add --include-transitive to the report |
Troubleshooting
| Symptom | Likely cause | Fix |
|---|---|---|
error NU1903: Warning As Error: Package '…' has a known high severity vulnerability | The package version has a published advisory, and warnings are errors | Move to a fixed version with --version |
dotnet package list --vulnerable prints the restore error, not the report | .NET 10 restores first, and that restore fails | Add --no-restore |
Unrecognized command or argument '-p:TreatWarningsAsErrors=false' | dotnet package list doesn't take MSBuild properties | Use --no-restore |
dotnet package add without --version fails with the same NU1903 | It restores the current, vulnerable state first | Name the safe version |
FAQ
The vulnerable package isn't one I referenced. What now?
Then it comes in through another package. Update that package first; if it has no fixed version yet, pin the transitive one, as in How to Upgrade a Transitive NuGet Package with Central Package Management.
Will this appear in CI even if it built yesterday?
Yes. Advisories are published after packages are, so the same code can fail tomorrow. That's the audit doing its job: update and rebuild.
Conclusion
NU1903 means NuGet Audit found a high-severity advisory for a package version in your project, and TreatWarningsAsErrors made it stop the restore. Get the full report with dotnet package list --vulnerable --no-restore, read the advisory, and move to a fixed version with an explicit dotnet package add <id> --version <safe version>; then the report comes back clean and the build passes.
