Fixed: "ERROR 2026 (HY000): SSL connection error" with "tlsv1 alert protocol version" in MySQL

tlsv1 alert protocol version is the server telling the client that it won't use that TLS version. The two have nothing in common, and the fix is to find what each allows.
What I Was Doing
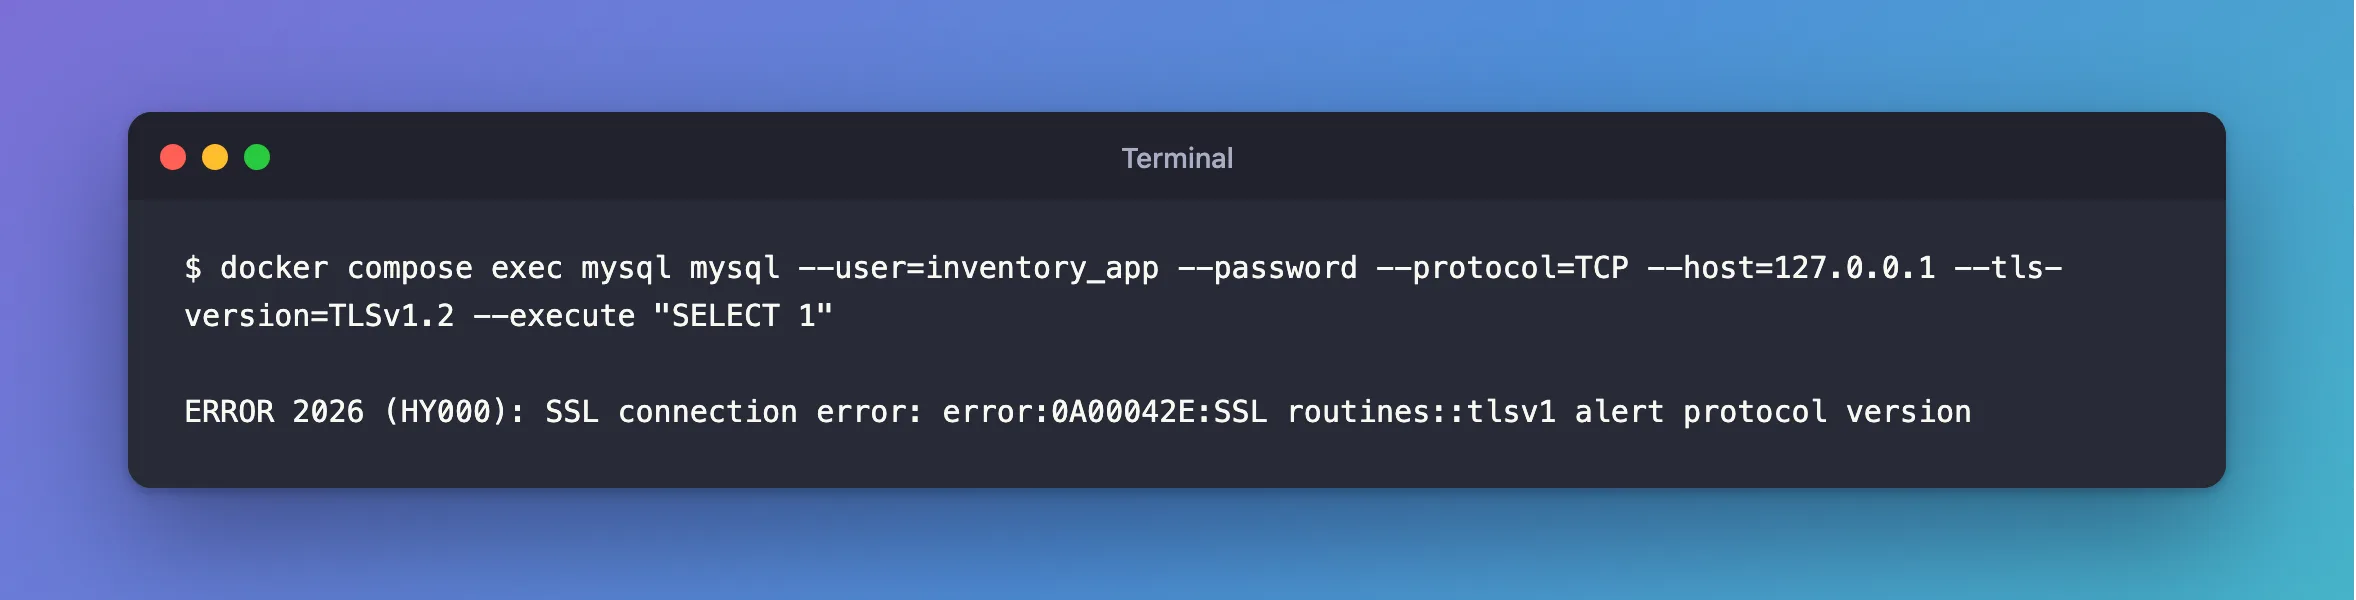
I'd set a MySQL 9.7 server to accept only TLS 1.3, and tried connecting with the mysql client, asking for TLS 1.2:
docker compose exec mysql mysql --user=inventory_app --password --protocol=TCP --host=127.0.0.1 --tls-version=TLSv1.2 --execute "SELECT 1"
What I Expected
For this test, a refusal. If you've landed here, either someone tightened the server's setting, or your client has an old list.
What I Got
ERROR 2026 (HY000): SSL connection error: error:0A00042E:SSL routines::tlsv1 alert protocol version
What I Checked
What the server allows, in a session over the local socket, which needs no TLS:
SHOW VARIABLES LIKE 'tls_version';
+---------------+---------+
| Variable_name | Value   |
+---------------+---------+
| tls_version   | TLSv1.3 |
+---------------+---------+
1 row in set (0.001 sec)
What the client asked for: only TLS 1.2. Those two lists don't overlap.
Why It Happens
The client offers its versions at the start of the handshake. If the server can't accept any, it sends this alert. tlsv1 here is only part of the alert's name, and doesn't mean TLS 1.0.
The Fix
Use a version from the server's list. For the mysql client, that means removing --tls-version, or naming one the server allows:
docker compose exec mysql mysql --user=inventory_app --password --protocol=TCP --host=127.0.0.1 --tls-version=TLSv1.3 --table --execute "SHOW SESSION STATUS LIKE 'Ssl_version'"
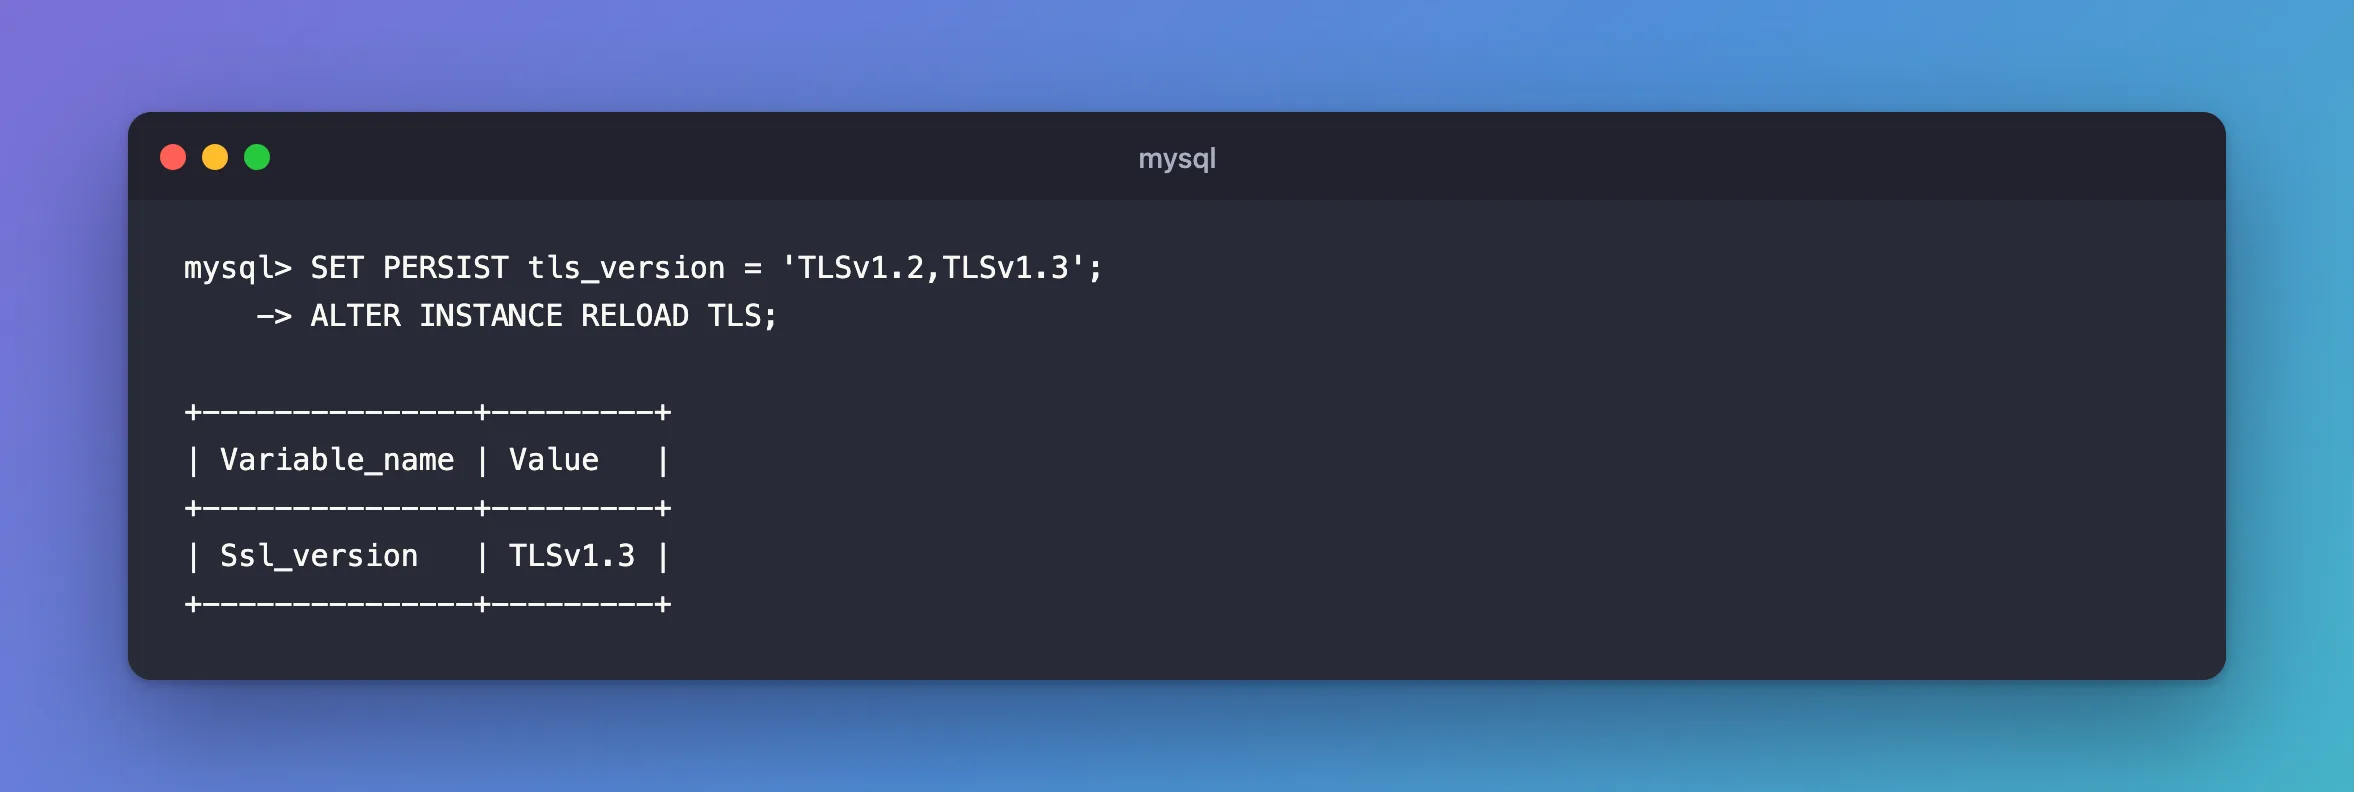
For an older client that can't do TLS 1.3, widen the server's list instead:
SET PERSIST tls_version = 'TLSv1.2,TLSv1.3';
ALTER INSTANCE RELOAD TLS;
After the Fix
+---------------+---------+
| Variable_name | Value   |
+---------------+---------+
| Ssl_version   | TLSv1.3 |
+---------------+---------+
Common Mistakes
| Mistake | What happens | Do this instead |
|---|---|---|
Reading tlsv1 as TLS 1.0 | You look for a problem that isn't there | Read it as the alert's name |
| Turning TLS off to get in | It may be refused too, and it's unencrypted | Find a common version |
| Changing the server's list and not reloading | The old list stays in force | Run ALTER INSTANCE RELOAD TLS |
Troubleshooting
| Symptom | Likely cause | Fix |
|---|---|---|
From .NET: Cannot determine the frame size… | The same mismatch | The fix |
ERROR 3159 | The server wants TLS, and the client has none | The fix |
tls_version says both, and it's still refused | The server hasn't reloaded | Check Current_tls_version |
Conclusion
This alert means no TLS version in common. Compare tls_version on the server with what your client asks for, and use one on both lists.
Additional Resources
- Encrypted Connection TLS Protocols and Ciphers — both sides of this.
- Command Options for Encrypted Connections —
--tls-version.
